Alternatives
Dependency-Track alternatives
Dependency-Track is free, open source and good at what it does. Teams look elsewhere when they want someone else to run it, need supplier SBOM workflows, or realize the real problem is the SBOMs going in.
Updated
We build CRACI, so weigh that in; we describe every option from its own documentation and say when another tool fits better.
Why teams look for alternatives
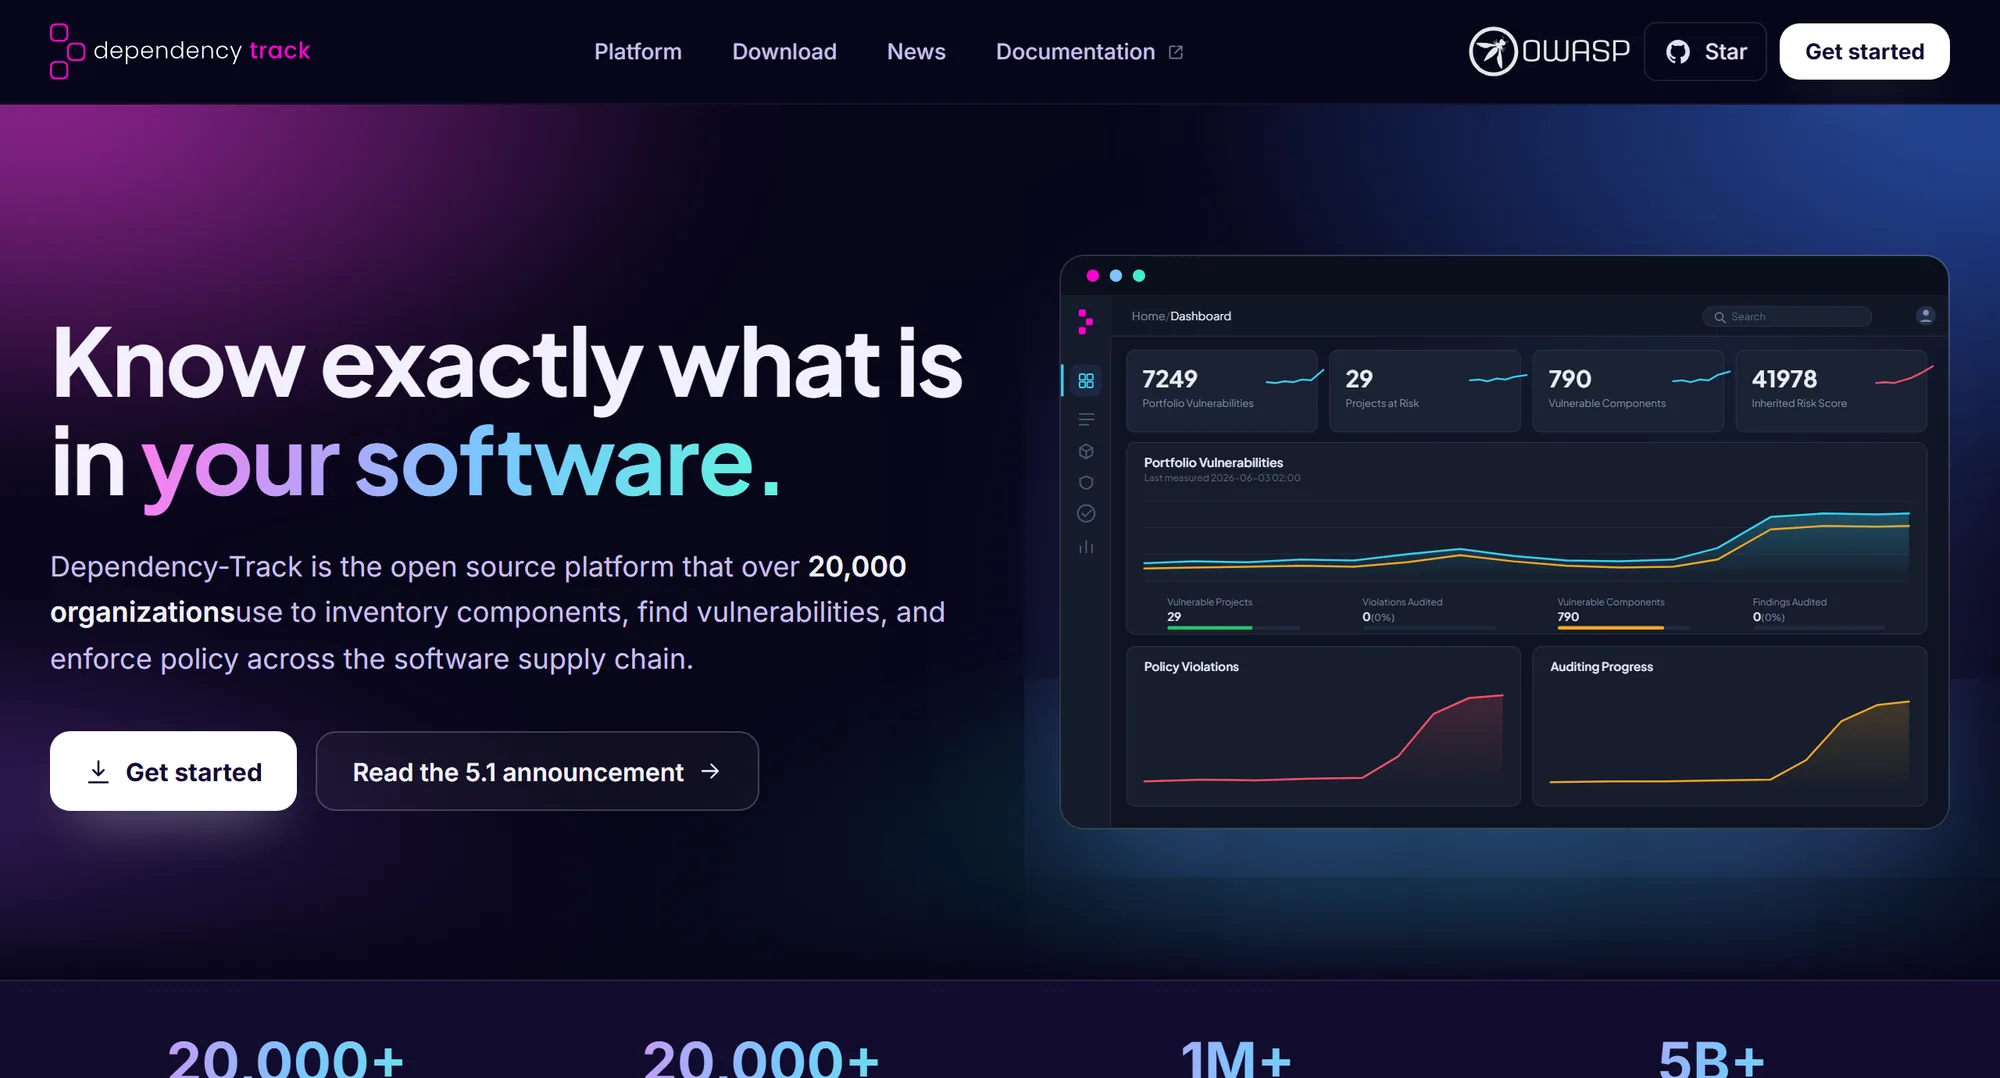
OWASP Dependency-Track is open source under the Apache 2.0 license. It tracks component usage across every version of every application in a portfolio, pulls vulnerability intelligence from sources including the National Vulnerability Database and GitHub Advisories, applies security, license and operational policies, and consumes and produces CycloneDX VEX. Pipelines upload SBOMs to it through its API. For many teams it is the right answer, and it costs nothing to license.
The reasons teams look further are usually about scope and fit:
- You would rather not operate it. Dependency-Track is self-hosted, so you run the server, the upgrades and the backups.
- You need supplier workflows. Collecting SBOMs from vendors, analyzing vendor binaries, or sharing SBOMs with customers are jobs some commercial platforms are built around.
- You need license compliance with legal output, such as attribution notices.
- You do not trust the input. Dependency-Track analyzes the SBOMs it receives; it does not generate them. If the generator misses a dependency, so does every finding downstream.
What to look for
- Where the SBOM comes from: generated by the platform, imported, or recorded from the build.
- Whether anything tells you how complete an SBOM is.
- VEX, triage and policy workflows, if your security team lives in them today.
- License analysis and attribution.
- Who operates it, and whether you can self-host or run air-gapped.
- Supplier SBOM intake and sharing with customers or authorities.
The options
CRACI (our product)
CRACI is not a portfolio analysis platform. It is a GitHub Actions-compatible runner: you change
runs-on to craci, and a package-aware proxy records what each job fetches from package
sources, including packages restored from CI caches. The SBOM, in CycloneDX or SPDX, comes from that record, with a
completeness state per job and per cache. CRACI monitors
those SBOMs for new vulnerabilities, and the API returns SBOMs, network traces and provenance.
CRACI's inventory view shows exactly which software versions are deployed to which products, globally.
Best for: teams on GitHub Actions whose problem is the input. CRACI produces the SBOM in the build and monitors it, so there is no generator to run and no upload step to maintain.
Consider if: you want build evidence and egress control at the source. CRACI lets security teams triage findings, route them to the right team and record VEX. CRACI's policy gates can block a build, and it enforces license policy. CRACI runs on GitHub Actions only today, with GitLab CI and Jenkins on the roadmap.
CRACI for Dependency-Track users
Anchore Enterprise
Anchore Enterprise builds on Anchore's open-source Syft and Grype. It generates SBOMs from container images, source and filesystems, imports SBOMs created elsewhere, rescans stored SBOMs without the original artifact, and enforces policy packs for FedRAMP, NIST, CIS, PCI DSS and CMMC. It deploys on Kubernetes, Docker Compose or air-gapped, with integrations for GitHub, GitLab, Jenkins, AWS CodeBuild and Azure Pipelines. Pricing is by quote.
Best for: container fleets across several CI systems, and government or air-gapped environments.
Consider if: you want a commercial platform you still run yourself. If you only need generation and matching, Syft and Grype are free.
FOSSA
FOSSA started with open-source license compliance: full-text license detection, automatic policies and attribution notices. It produces and consumes SBOMs in SPDX and CycloneDX, optionally with VDR or VEX statements, enforces NTIA and FDA minimum elements on imported SBOMs, and on Enterprise shares SBOMs through an SBOM Portal. The Free plan runs as multi-tenant SaaS; Business is $20 per project per month, billed annually (as of September 2026).
Best for: teams where license risk and supplier SBOMs are the main concern.
Consider if: you want a hosted platform and a free way to start.
Cybeats SBOM Studio
SBOM Studio calls itself "the SBOM system of record." It stores SBOMs from your products and suppliers, supports SPDX 2.2 to 3.0.1 and CycloneDX 1.2 to 1.7, validates files with an SBOM Quality Score, matches every component continuously against vulnerability intelligence, handles VEX and license analysis, and shares SBOMs with customers, including over the Transparency Exchange API. For generation, Cybeats points to its Marketplace of tool vendors.
Best for: central product security teams in ICS and OT, medical devices, telecom and automotive.
Consider if: you run an SBOM program across many products and suppliers.
Manifest
Manifest creates, imports, enriches and shares SBOMs across your products, your vendors' software and your AI models. Vendors upload SBOMs through a portal, and when a vendor provides none, Manifest can generate one from the compiled binary. It turns findings into tickets and supplier outreach, supports VEX, and its CLI works in any CI, with a GitHub Action that runs Syft by default.
Best for: organizations whose main exposure is software they buy.
Consider if: third-party risk and AI model inventories matter as much as your own builds.
ONEKEY
ONEKEY is a product cybersecurity and compliance platform for connected devices. You upload a firmware image, and it analyzes the binary, with no source code needed, to find components, known vulnerabilities and likely zero-days such as hardcoded credentials. It generates an SBOM from the binary, imports SBOMs from source scanners or suppliers, exports CycloneDX and SPDX, and re-analyzes uploaded firmware daily. Its Compliance Wizard covers the Cyber Resilience Act, IEC 62443-4-2, ETSI EN 303 645 and the Radio Equipment Directive.
Best for: device makers who need to analyze firmware, including supplier blobs they never built.
Consider if: your products are connected devices rather than web services.
SBOM Observer
SBOM Observer, from the Swedish company Bitfront AB, ingests, normalizes and versions SBOMs, runs policy checks, tracks vulnerabilities across components, and produces compliance evidence. It works with SPDX, CycloneDX and VEX, runs as SaaS or on-premise, optionally air-gapped, and comes with free tools such as an open-source CLI and the SBOM.link viewer. As of September 29, 2026, Business is about $80 (€69) per user per month with up to 10 projects, and Enterprise, for 25 users or more, is priced on request.
Best for: teams that want Dependency-Track's job as a managed service with published prices.
Consider if: per-user pricing and the project limits per plan fit your portfolio.
sbomify
sbomify generates SBOMs in CI through its open-source GitHub Action, manages them across releases, and shares them and compliance documents through a branded Trust Center, including over the Transparency Exchange API. It supports CycloneDX and SPDX and integrates with Google OSV and Dependency-Track for analysis. It is open source and can be self-hosted. As of September 2026, the Community plan is free for 1 product and 5 components with public documents only, and Business is $159 per month billed annually.
Best for: teams that need to share SBOMs with customers, not only analyze them.
Consider if: you want to keep Dependency-Track for analysis; sbomify integrates with it.
Side by side
| Capability | CRACI | Dependency-Track | Anchore Enterprise | FOSSA | Cybeats | Manifest |
|---|---|---|---|---|---|---|
| Produces the SBOM | Recorded during the build | Analyzes uploads | Scans images and files | FOSSA CLI | Via Marketplace vendors | Syft by default |
| Completeness state per job | Quality Score checks format | |||||
| Imports third-party SBOMs | Vendor SBOMs can be added | |||||
| Continuous vulnerability monitoring | ||||||
| Policy engine | Policy gates and license policy | Not stated | ||||
| VEX | ||||||
| License compliance | License policy can block a build | Not stated | Not stated | |||
| Runs your builds, with egress policy | Jobs run on CRACI runners | |||||
| Who operates it | CRACI (managed) | You (self-hosted) | You, including air-gapped | FOSSA (SaaS) | Not stated | Not stated |
| Price (September 2026) | Pay per build minute, no monthly fee | Free, Apache 2.0 | Quote | Free plan; Business $20 per project per month | Not stated | Not stated |
- Included
- Partly
- Not included
"Not stated" means we could not find it in the vendor's public pages. The table covers Dependency-Track and the first five options; ONEKEY, SBOM Observer and sbomify are described above. Every platform except CRACI analyzes SBOMs produced by something else, or generates them with a scanner or from a binary, so the quality of that input still matters whichever you pick.
Dependency-Track vs Dependency-Check
The names are close, and both are OWASP projects, but they do different jobs. Dependency-Track's own documentation compares them:
- What it is. Dependency-Track is a platform. Dependency-Check is a library with a command line interface, build plugins for tools such as Maven and Ant, and a Jenkins plugin.
- How it works. Dependency-Track starts from an SBOM, generated at build time or obtained from a vendor. Dependency-Check scans files on the filesystem and extracts evidence with varying degrees of confidence.
- Matching. Dependency-Track matches precisely via the NVD and other sources. Dependency-Check uses fuzzy matching via the NVD.
- Results. Dependency-Track serves metrics through a web interface and REST API, with an auditing workflow per project and across the portfolio. Dependency-Check writes a static HTML, XML, JSON or CSV report per project.
In short, Dependency-Check is a scanner and Dependency-Track is where SBOMs are analyzed over time. Neither records what your build fetched.
A note on the Cyber Resilience Act
If the CRA is why you are reviewing your SBOM tooling, the reporting obligations apply from September 11, 2026, with an early warning due within 24 hours of becoming aware of an actively exploited vulnerability. Meeting that depends on knowing which releases contain the affected component, which depends on the SBOM for each release being right. Anchore, FOSSA, Cybeats and Manifest all publish CRA material. CRACI automates a significant part of the software supply chain visibility and evidence that companies need for their wider CRA compliance process. No platform on this page makes a product compliant on its own.
When to stay with Dependency-Track
- You are comfortable operating it, and a free, open-source, self-hosted platform fits your policy.
- Your security team relies on its policy engine, VEX and portfolio views.
- Your real gap is SBOM quality. Fix the input instead, and keep the analysis you have.
For more on the input side, read about build-time SBOM generation and CRA compliance.
Dependency-Track alternatives FAQ
Short answers to the questions teams ask when they compare
What is Dependency-Track?
OWASP Dependency-Track is a free, open-source platform under Apache 2.0 that analyzes SBOMs. It tracks the components in every version of every application in a portfolio, matches them against vulnerability sources such as the NVD and GitHub Advisories, applies security, license and operational policies, and consumes and produces CycloneDX VEX. It does not generate SBOMs; pipelines upload them through its API.
What is dependency tracking?
Dependency tracking means keeping a record of the third-party components each version of your software uses, and checking that record continuously against vulnerability data and policy. When a new advisory lands, it tells you which releases contain the affected component. The record is usually an SBOM per release.
How do you run Dependency-Track?
Its documentation recommends Docker Compose: download the docker-compose.yml from dependencytrack.org and run docker compose up -d. The API server needs at least 2 GB of RAM. See docs.dependencytrack.org for production setups.
What is the difference between Dependency-Track and Dependency-Check?
Dependency-Track is a platform that analyzes SBOMs across a portfolio and serves results through a web interface and REST API. OWASP Dependency-Check is a command line tool and set of build plugins that scans files on disk, matches them to vulnerabilities with fuzzy matching via the NVD, and writes a static report per project.
Is there a hosted alternative to Dependency-Track?
Yes. FOSSA runs as SaaS, SBOM Observer offers SaaS or on-premise, and sbomify has a cloud service with a free Community plan. CRACI is managed too, and produces the SBOM from the build instead of waiting for an upload.
Start with a better SBOM
Run one GitHub Actions workflow on CRACI and compare its SBOM with the one you upload to Dependency-Track today.
Book a demo